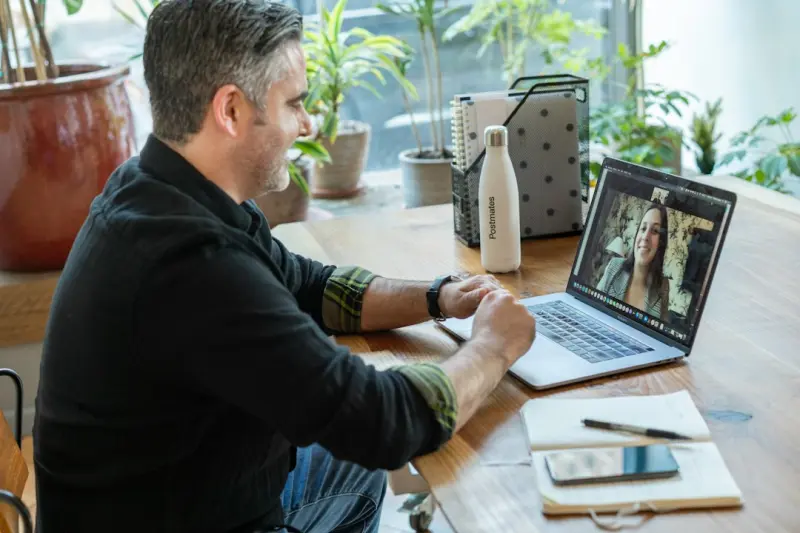
When the pandemic forced offices onto screens and desks into living rooms, the conversation shifted from “how do we work remotely?” to “how much can we watch our employees while they work from home?” As a lawyer who’s spent a decade navigating the gray zones of technology, privacy, and employment law, I’ve watched the balance tip and wobble in ways that would make a tightrope walker nervous. Employers are eager to protect assets, ensure productivity, and mitigate risk, but the tools they deploy—screen‑recording software, keystroke loggers, GPS trackers—often blur the line between legitimate oversight and invasive surveillance.
Why the Legal Landscape Is Changing Now
The rapid adoption of remote‑work technologies has outpaced the statutes designed to regulate them. In Canada, the Personal Information Protection and Electronic Documents Act (PIPEDA) sets baseline expectations for how private-sector organizations handle personal data, but it was drafted in an era when “the office” meant a physical space with a door you could lock.
Since then, two forces have converged:
- Technological acceleration: AI‑powered analytics can now parse an employee’s mouse movements, facial expressions, and even background noise to infer engagement levels.
- Regulatory momentum: Provinces such as British Columbia and Quebec have introduced or are contemplating stricter privacy statutes that explicitly address digital monitoring.
These shifts mean that what was once a “nice‑to‑have” productivity tool can quickly become a legal liability. Companies that ignore the nuance risk fines, class‑action lawsuits, and a bruised employer brand.
The Core Principles Courts Keep Returning To
When judges evaluate whether an employer’s monitoring regime is lawful, they typically weigh three pillars:
- Legitimate purpose: The surveillance must serve a clear, lawful objective—such as protecting confidential information or ensuring workplace safety.
- Proportionality: The intrusion must be no greater than necessary to achieve that purpose. Monitoring every keystroke for an hour a day, for example, may be deemed excessive.
- Transparency: Employees must be informed—preferably in plain language—about what is being collected, how it will be used, and who will have access.
These principles echo the reasoning found in Digital Evidence and Remote Hearings: Canada’s Courts Enter a New Era, where judges stressed that any digital intrusion must be justified, proportionate, and disclosed.
Common Monitoring Tools and Their Legal Risks
Below is a snapshot of the most popular monitoring solutions and the specific pitfalls they present under current Canadian privacy law.
- Screen‑capture software: Captures periodic screenshots. Risk: If images contain personal or non‑work‑related content (e.g., a family photo), it may constitute an unlawful collection of private data.
- Keystroke logging: Records every key pressed. Risk: Capturing passwords or personal messages can trigger severe penalties under PIPEDA.
- Web‑activity trackers: Logs visited URLs. Risk: Over‑broad logging of non‑work sites can be seen as an unreasonable invasion of privacy.
- GPS and location services: Tracks device location. Risk: Continuous location data may be deemed excessive unless tied to a safety‑critical role.
- AI‑driven sentiment analysis: Analyzes tone in video calls. Risk: Subjectivity in interpreting “engagement” can lead to discrimination claims if used to make employment decisions.
Each of these tools can be defensible if deployed with clear policies, limited scope, and strong data‑security safeguards. The key is to align technology with the three judicial pillars mentioned earlier.
Crafting a Privacy‑First Monitoring Policy
Below is a step‑by‑step framework that helps organizations design a policy that satisfies both business needs and legal obligations.
- Define the business objective. Ask yourself: What specific risk am I trying to mitigate? If it’s protecting trade secrets, a limited data‑loss‑prevention (DLP) solution may suffice without full‑screen capture.
- Conduct a privacy impact assessment (PIA). Map out what data will be collected, how long it will be retained, and who can access it. This exercise is mandatory under many provincial statutes.
- Limit collection to the minimum necessary. Use “privacy by design” principles—disable features that capture non‑work‑related content, set reasonable time windows, and anonymize data where possible.
- Draft clear, concise employee notices. Avoid legalese. A short FAQ that explains what is monitored, why, and how employees can raise concerns goes a long way toward transparency.
- Secure the data. Encrypt stored logs, enforce strict access controls, and establish a retention schedule that aligns with the original purpose.
- Provide a grievance mechanism. Employees should have a safe channel to dispute perceived overreach without fear of retaliation.
- Review and update regularly. Technology evolves fast; so should your policies.
When you embed these steps into your compliance routine, you’re not just checking a box—you’re building trust.
When AI Enters the Monitoring Room
Artificial intelligence is the new frontier of employee oversight. Tools that flag “disengaged” facial expressions or predict “burnout risk” sound futuristic, but they also raise complex legal questions about bias, accuracy, and the right to mental‑health privacy.
In my recent research, I found that the upcoming Artificial Intelligence and Data Act (AIDA)—still in the proposal stage—will likely impose stricter standards on AI systems that affect individuals, including employees. Companies that lean on AI for monitoring should therefore:
- Validate algorithms for fairness and avoid disparate impact on protected groups.
- Maintain human oversight; never let an algorithm make final employment decisions without a qualified reviewer.
- Document the AI’s decision‑making process to demonstrate compliance if regulators knock on the door.
For a broader view on how AI reshapes legal practice, see Why Generative AI Is Redrawing the Boundaries of Legal Practice. The same caution that applies to client‑facing AI tools applies to internal employee surveillance.
Cross‑Border Considerations for Multinational Teams
Many Canadian firms now employ talent across the United States, the United Kingdom, and beyond. When you monitor an employee located outside Canada, you must also respect the privacy regimes of that jurisdiction—think the EU’s GDPR, California’s CCPA, or Brazil’s LGPD.
Key takeaways:
- Data residency: Storing monitoring logs on servers located in a foreign country may trigger export‑control rules.
- Consent standards vary: Some regimes require explicit, opt‑in consent for any form of biometric monitoring, while others accept opt‑out.
- Enforcement landscape: Regulators in the EU are known for heavy fines; a misstep could cost millions.
Pragmatically, adopt the most stringent standard across the board. It simplifies compliance and demonstrates a commitment to employee privacy, no matter where they log in from.
The Bottom Line: Turn Risk into Competitive Advantage
Privacy‑forward monitoring isn’t a hindrance; it can be a differentiator. Companies that respect boundaries often see higher morale, lower turnover, and a stronger employer brand—factors that attract top talent in a tight labor market.
Here’s a quick checklist you can share with leadership:
- ✅ Conduct a privacy impact assessment for every monitoring tool.
- ✅ Draft a transparent policy with employee-friendly language.
- ✅ Limit data collection to what’s strictly necessary.
- ✅ Secure and encrypt all logs; set clear retention periods.
- ✅ Provide a clear, safe avenue for employee concerns.
- ✅ Review AI‑driven tools for bias and maintain human oversight.
- ✅ Align with the toughest applicable privacy law—often GDPR‑level standards.
By embedding these practices, you protect your organization from costly lawsuits, safeguard employee trust, and future‑proof your remote‑work strategy.
Looking Ahead: Emerging Trends to Watch
As we look toward the next wave of legal developments, keep an eye on these emerging trends:
- Legislative proposals for “digital workplace rights” that could grant employees explicit control over their data.
- Increased use of blockchain for audit trails, ensuring any data access is immutable and traceable.
- Greater emphasis on mental‑health privacy, with potential new statutes limiting the use of emotion‑recognition software.
Staying ahead means partnering with legal counsel early, investing in privacy‑by‑design technology, and fostering a culture where employee dignity is as important as data security.
Remote work isn’t going anywhere, and neither is the temptation to peek behind the virtual curtain. The smarter, more compliant path is to set clear boundaries, be transparent, and treat privacy as a core component of your company’s values—not an afterthought.
Related Posts
When Algorithms Write Contracts: Navigating Legal Risks and Rewards
AI‑generated contracts promise speed and cost savings, but they also introduce hidden liability tr... Read More
When Algorithms Judge: Navigating AI’s Role in Modern Courtrooms
A deep dive into AI’s growing influence on courts, examining bias, transparency, and the steps law... Read More
Navigating Defamation in the Age of TikTok and Twitter
A fresh look at how social media reshapes defamation law, with actionable tips for individuals and b... Read More
Top Posts
Mark Daniels’ Guide to the Hottest Travel Trends of 2026
Mark Daniels explores the latest travel trends—from bite‑size getaways and eco‑friendly lodging to vibrant food festivals and waterfront adventures—offe...Read More
Why Enterprise Knowledge Bases Are the Next Growth Engine
Turning internal knowledge into a revenue engine can transform a SaaS business. Learn how premium content, market‑intelligence services, and white‑label pla...Read More
Why Data Sovereignty Is the New National Imperative for Canadian SaaS Leaders
Data sovereignty isn’t just a legal checkbox; it’s a strategic lever for Canadian SaaS firms. Learn how internal marketplaces and AI negotiation bots can he...Read More
Beyond the Plate: Crafting Conversation‑Centric Dining Experiences
Explore how thoughtful seating, sound, and community events transform dining into a conversation‑rich experience, fostering deeper connections and lasting loy...Read More
0 Comments
Post Comment
You will need to Login or Register to comment on this post!